
Firewall-as-a-Service (FWaaS)
Your firewall, delivered from the cloud.
FWaaS delivers firewall and network security as a cloud service.
Today’s Challenges
Legacy firewalls can’t keep up.

Appliance scaling limits
Physical and virtual firewalls run out of compute — TLS inspection, CPU load, and packet drops force mid-term hardware replacement.
Appliance limits
Config sprawl
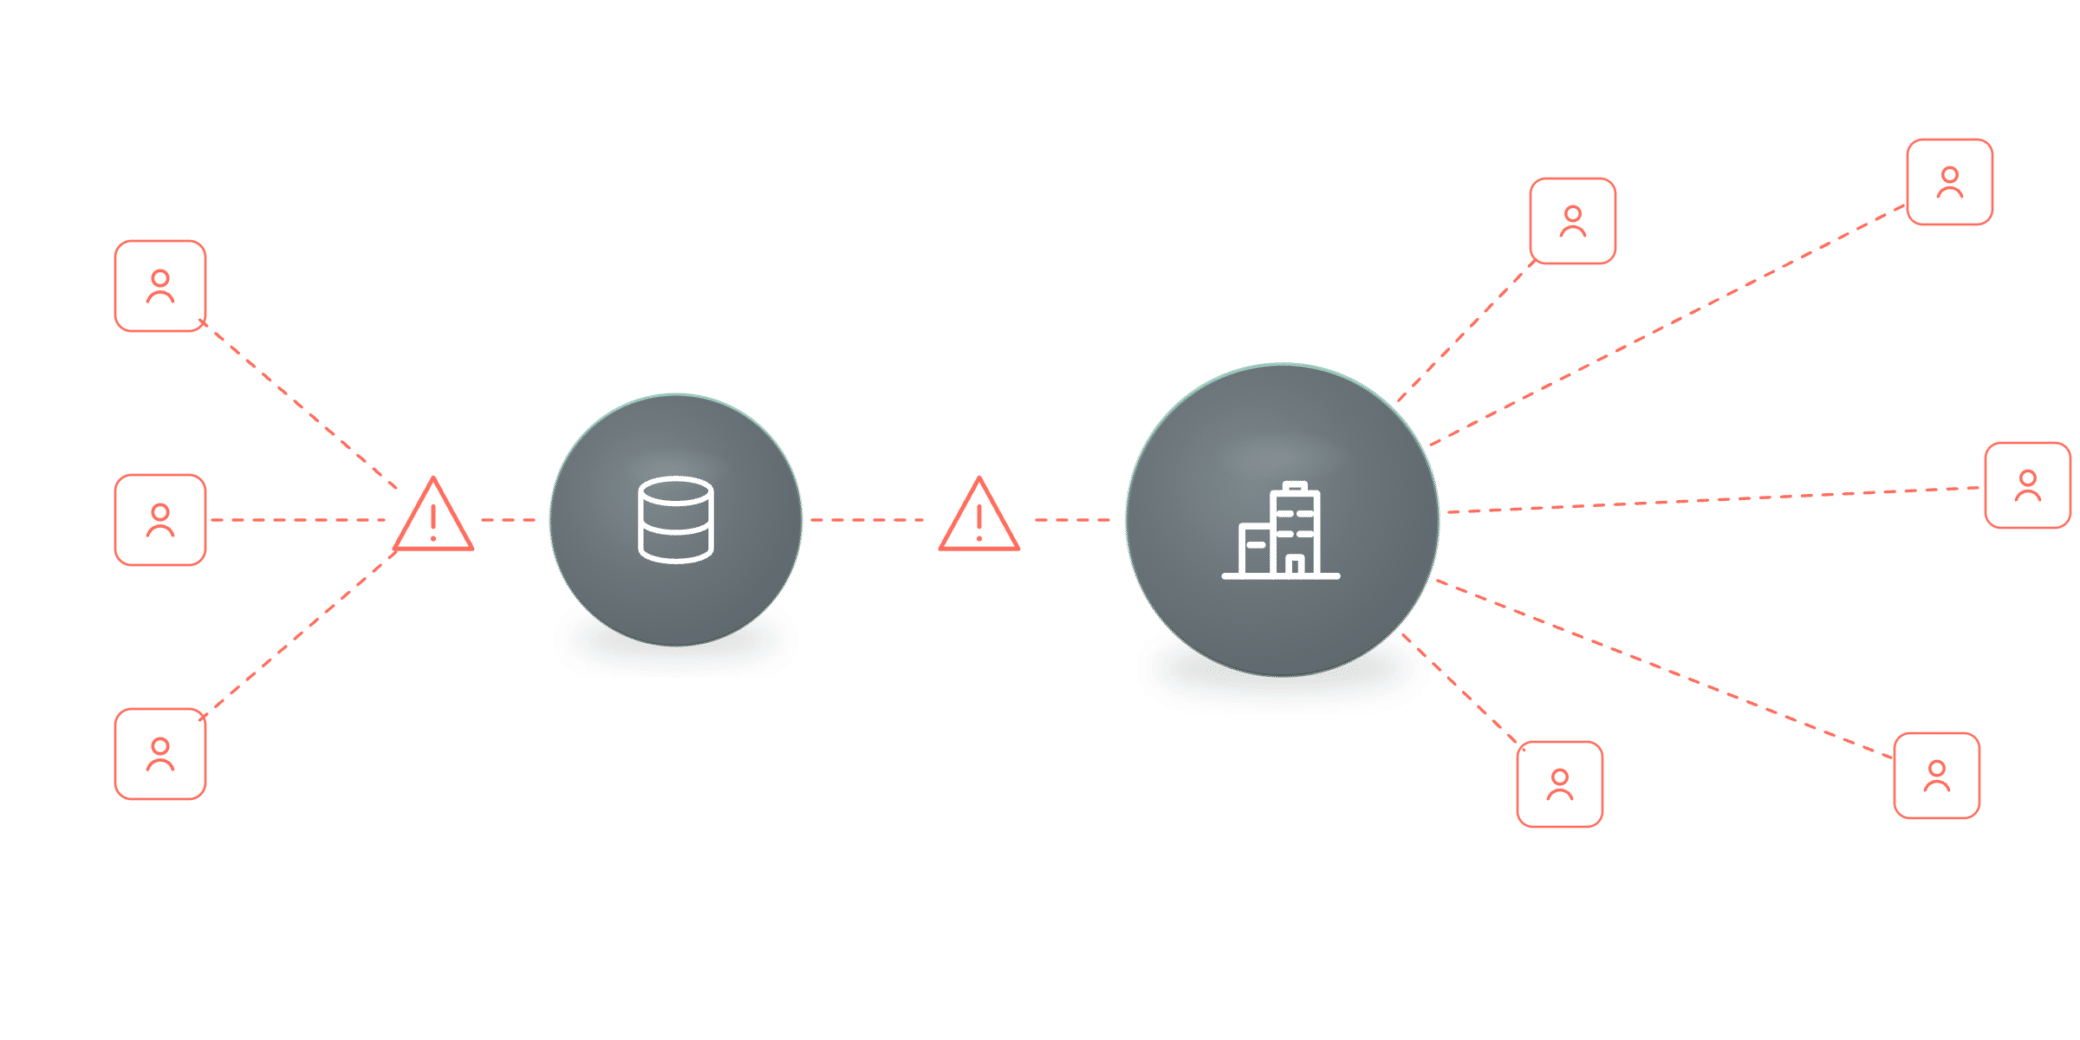
Lateral movement
Our Approach
One firewall. Everywhere.
Cato delivers firewall as a service from a single cloud-native platform — replacing branch, data center, and LAN firewalls with one always-on engine. Every user, site, and cloud is governed by the same policy and inspected at full throughput, with no limits on ports, protocols, or encryption, so protection scales with your business instead of your hardware.


Converge in the cloud
Replace branch, data center, and LAN firewalls with a single cloud-native FWaaS — no hardware to size or patch.

Detailed analysis and reporting
Get full visibility into every flow with detailed analytics and reporting across users, sites, and clouds.

Enforce one policy everywhere
Apply consistent access control and zero trust across every user, site, and environment.
eBook
Real-World Business Value with FWaaS
How it works
Firewall-as-a-Service (FWaaS) Capabilities
North-south, east-west, and LAN
Full traffic inspection without blind spots
Inspect all traffic with no limits on ports, protocols, or encryption.
Inspect internet, WAN, and LAN traffic — no blind spots
Multi-gig throughput from the cloud
Replace branch, data center, and LAN firewalls
Identify apps and users
DPI-based application and user awareness
A DPI engine identifies the application as early as the first packet, without decrypting the payload.
Built-in awareness of thousands of applications
Identify apps on the first packet, no decryption
Tie a user identity to every network flow
See it in action
Watch how Cato does it

Firewall-as-a-Service Demo Video
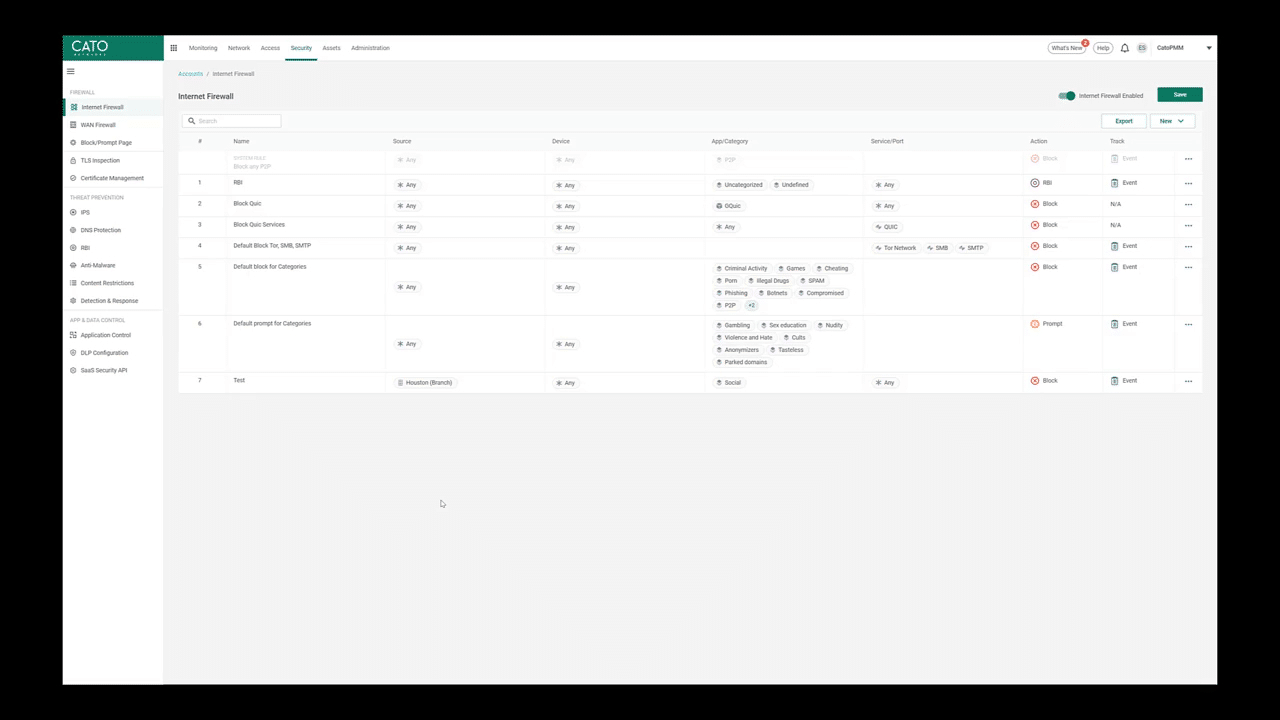
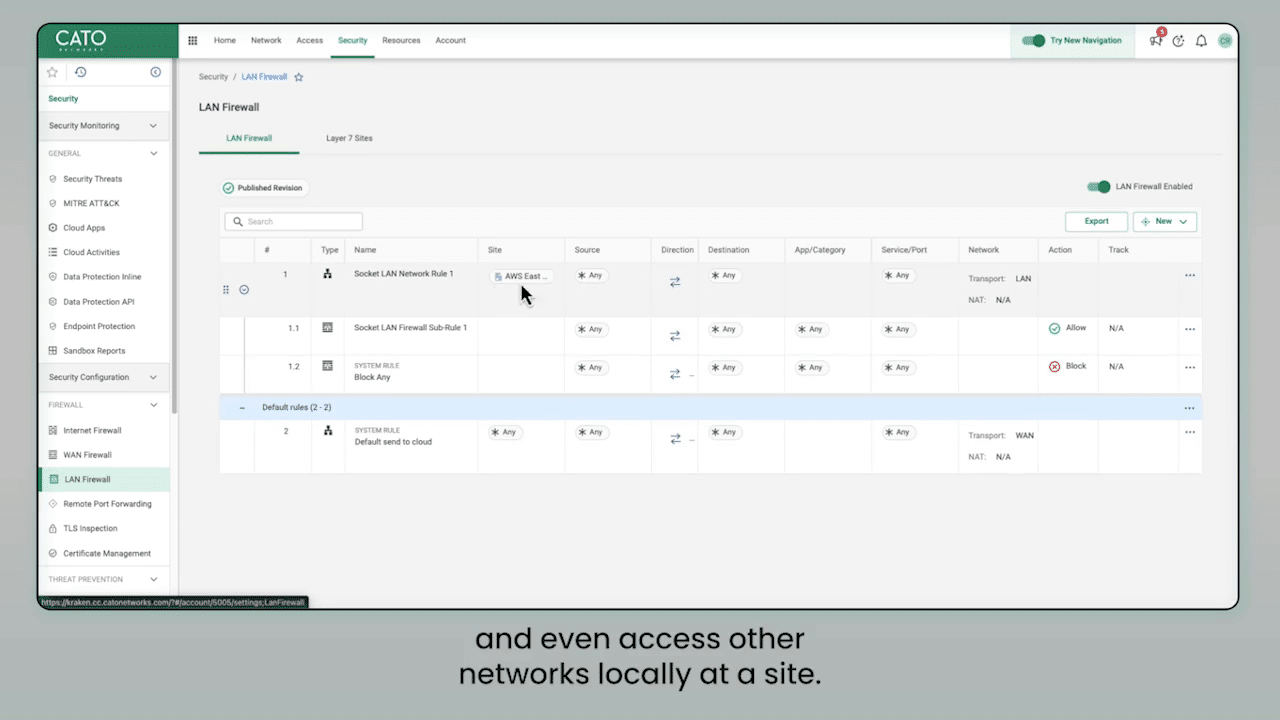
Protect Local Networks with Cato’s Application-Aware LAN Firewall
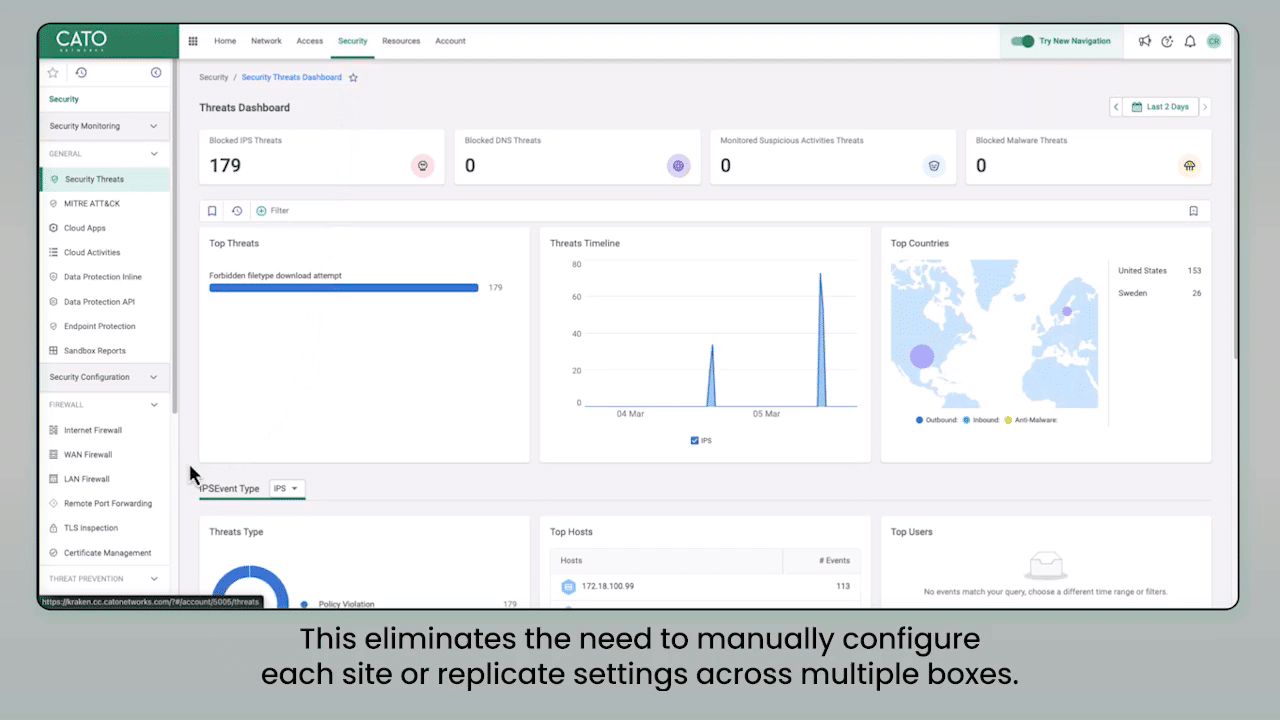
Microsegmentation That Stops Lateral LAN Threat Movement with the Cato LAN Firewall
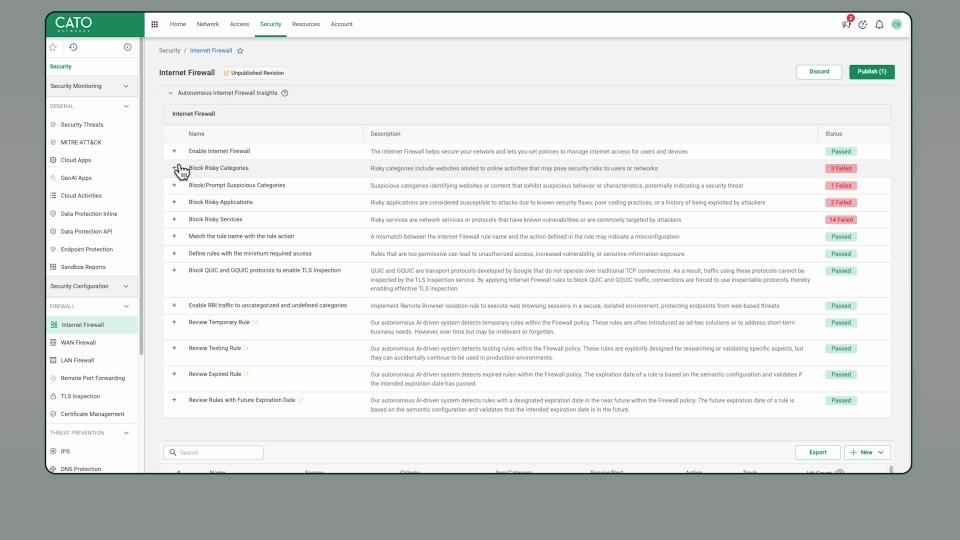
The new Autonomous FW Policies demo
Customer Stories
Customers love Cato
“
We had five different firewall vendors across our locations, and none of them were talking to each other. When your tools don’t integrate, you can’t see the full picture—and the gaps you can’t see are exactly where the risk is.
Douglas Arnn
Director of IT Infrastructure, Trimark

Director, IT Infrastructure
Healthcare Education Institution

Wood Compere
Southwest Behavioral & Health Services
IT Leader
Engineering Consultancy
Mark Dela Cruz
IT Infrastructure Head, Standard Insurance
Get a live demo
Secure every interaction across the enterprise, cloud, and AI with the only purpose-built SASE platform.
What to expect

15–30 minute session with a SASE product expert

Discuss your use cases and how we can help

Live product demonstration where applicable
Get Started
See Cato in Action
What’s new
Latest resources and insights


FAQS
Answers to common questions
How does Cato FWaaS inspect and scale firewall protection?3 questions
What is Firewall-as-a-Service (FWaaS) and how does it differ from traditional hardware firewalls?
FWaaS delivers firewall inspection and policy enforcement as a cloud service. With Cato, WAN and Internet traffic is enforced in global PoPs, while centrally managed Cato Sockets or vSockets connect sites and can enforce local LAN firewall policy. This reduces third-party appliance sprawl and life cycle work while maintaining consistent policy across distributed environments.
What traffic can Cato FWaaS inspect?
Cato applies distinct firewall policies to Internet, WAN, and LAN traffic. WAN and Internet traffic routed through the Cato SASE Cloud Platform is inspected and enforced in Cato PoPs. East-west traffic behind a site can be inspected locally by the Socket Next Gen LAN Firewall. Inspection of encrypted content requires TLS Inspection and follows configured and Cato-managed bypasses.
How does Cato scale firewall inspection as traffic grows?
WAN and Internet firewall inspection runs in Cato cloud PoPs, reducing the need to size and refresh separate security appliances for those functions at every site. Site connectivity and local LAN inspection still depend on the selected Socket or vSocket capacity. TLS Inspection is centrally configured and processed in the PoPs, subject to supported traffic and policy bypasses.
How does Cato FWaaS simplify firewall operations across a SASE architecture?5 questions
Who is Cato FWaaS designed for?
Cato FWaaS is designed for distributed enterprises that need consistent firewall control across branches, data centers, cloud resources, and remote users. It is especially useful for teams seeking to consolidate policy management, reduce appliance sprawl and operational overhead, and apply identity-aware and application-aware controls across WAN, Internet, and supported LAN traffic.
How does FWaaS compare to managing multiple firewall appliances across locations?
Cato centralizes WAN, Internet, and LAN firewall policies in the Cato Management Application and distributes enforcement through cloud PoPs and Cato Sockets. Teams manage one policy framework and shared traffic context instead of separate rulebases across multiple firewall products. This reduces operational complexity and policy inconsistency.
How does Cato help teams manage and optimize firewall policies across distributed environments?
Cato centralizes WAN, Internet, and LAN firewall policies in the Cato Management Application and distributes them to the relevant enforcement points. Autonomous Firewall Insights identifies unused, overly permissive, or conflicting rules and recommends improvements. Administrators review and apply the changes, retaining control over policy enforcement.
What logging and monitoring capabilities are available?
Administrators can configure firewall rules to generate events in the Cato Management Application, then search and analyze those events for rule activity and enforcement. Cato supports notifications through subscription groups, email, or webhooks and can export event data to supported SIEM platforms. Event availability and retention depend on account configuration.
How does Cato FWaaS fit into a broader SASE architecture?
Cato Firewall is a built-in capability of the Cato SASE Cloud Platform. It shares the Cato Management Application, traffic context, and cloud enforcement architecture with Cato networking and security services. This helps teams apply consistent controls and analyze activity across WAN, Internet, LAN, and remote-access use cases. Availability of services such as IPS, CASB, DLP, SWG, and ZTNA depends on subscribed capabilities.
How does Cato FWaaS apply context-aware access control and segmentation?2 questions
How does Cato FWaaS handle application and user identification?
Cato uses Layer 7 inspection and shared flow context to identify applications and, when identity context is available, users and groups. Policies can combine application, identity, destination, device posture, and other attributes. Identification occurs as the required flow information becomes available, so application-aware rules may require more than the first packet.
What access control and segmentation capabilities does the platform provide?
Cato supports granular access and segmentation policies using sites, networks, VLANs, hosts, users, groups, applications, services, and device posture where supported by the applicable policy. The Socket Next Gen LAN Firewall can enforce Layer 2 through Layer 7 controls for east-west traffic, helping limit unauthorized lateral movement and access to sensitive resources.


