Product Demo Contact us

AI Security for Agents

Agents act on their own. Keep them in bounds.

Cato secures local, custom, and managed AI agents across the enterprise. Discover, assess posture, and stop risky behaviors before they create business impact.
Decorative concentric ring artwork

Todayโ€™s Challenges

Autonomy is the new attack surface.

Prompt injection via untrusted inputs
Autonomous data exfiltration
Over-privileged, misconfigured agents
Unauthorized actions, no audit trail

Prompt injection via untrusted inputs

Agents can’t always tell trusted inputs from untrusted ones, so a crafted prompt turns the agent’s own autonomy against you.

Autonomous data exfiltration

Agents access and transmit sensitive data on their own, often without clear boundaries or user oversight.

Over-privileged, misconfigured agents

Agents can run with excessive permissions across enterprise systems. Any misconfiguration is a breach path.

Unauthorized actions, no audit trail

Agents act across tools, APIs, and MCP interactions with no consistent record of what they did, or why.

Prompt injection

Exfiltration

Over-privilege

No audit trail

Our approach

See every agent.
Govern every action.

AI agents now act with real autonomy and real privileges โ€” and most security tools canโ€™t see them. Cato gives you full visibility into every agent across your environment and governs what each one is allowed to do, so you can adopt agentic AI without losing control.

Play the video

Discover agents

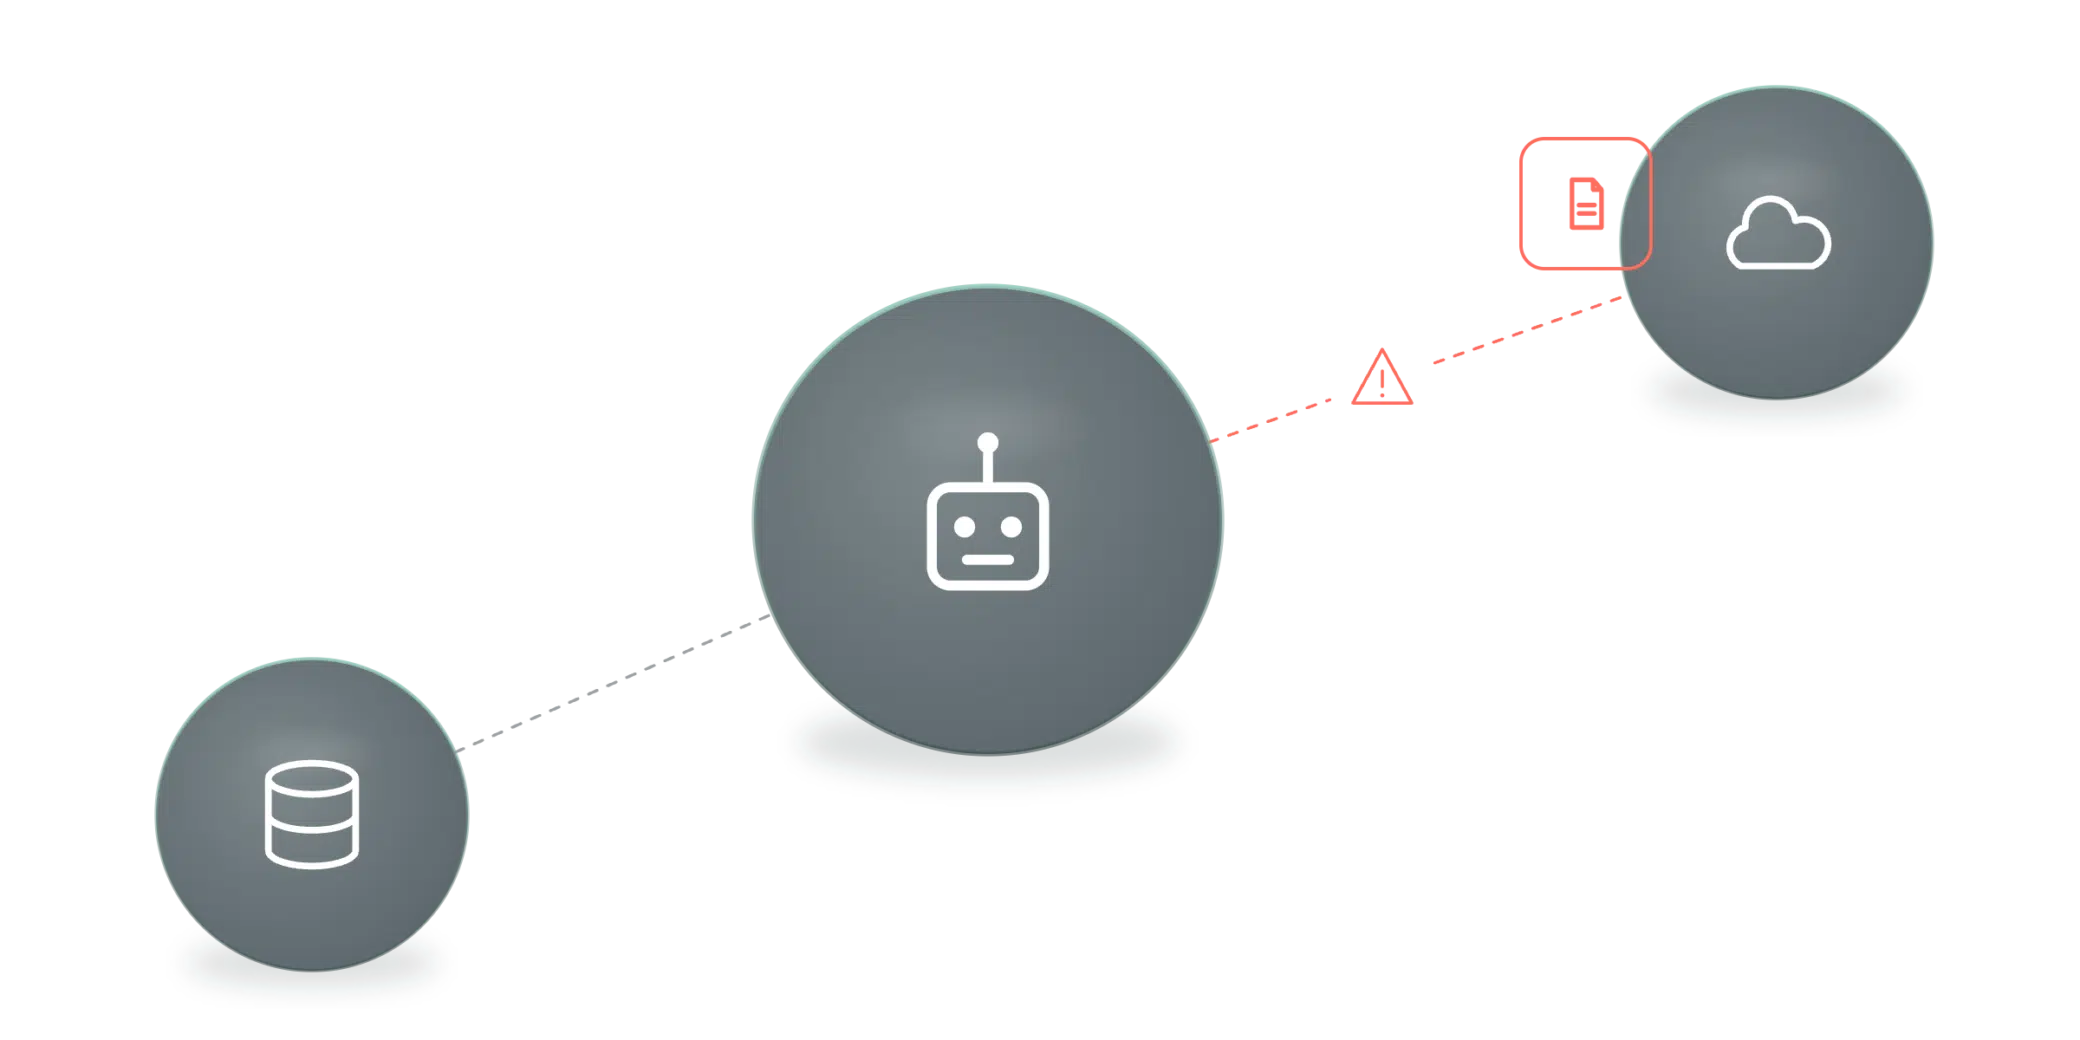
Cato connects to your infrastructure to discover AI agents across systems, tools, and MCP interactions.

Monitor behavior

Cato monitors agent behavior: prompts, tool calls, and actions: logging every interaction to assess risk.

Enforce runtime controls

Cato applies runtime controls to govern access and stop unauthorized or unsafe actions before execution.

Webinar

Defending Against the Next Generation of Agentic Attacks

How it works

AI Security for Agents Capabilities

Agent discovery

Discover agents across the enterprise

Security teams canโ€™t govern agents they canโ€™t see. Cato discovers local, custom, and managed agents across the enterprise, including their tools, MCP servers, data access, and execution paths.

Find local, custom, and managed agents

Map the tools, MCP servers, and data they access

Reveal execution paths so teams know where to focus

Posture & exposure

Assess agent posture and exposure

Agents often inherit broad permissions and unsafe tool access. Cato surfaces agent activity, tools, and MCP usage so teams can reduce exposure and define safe operating boundaries.

Surface agent activity, tools, and MCP usage

Spot over-privileged access and unsafe integrations

Define safe operating boundaries

AI Red Teaming

Red team agent behavior before it becomes action.

Test the models your agents use with contextual attack scenarios powered by Cato AI Labs. Map exposure, select the right models, and build policies for safe operating boundaries.

Test against realistic AI attacks built by Cato AI Labs.

Prioritize risks by realistic impact and governance frameworks.

Enable AI governance reviews and mitigate risk in the same solution.

AI Security Engine

Detect AI-native risk with the AI Security Engine

Protect agents with the Cato AI Security Engine, which detects AI-native risk with industry-leading precision, recall, and low latency while evaluating context across the full interaction.

Detect AI-native risk with high precision and recall

Evaluate context across the full interaction

Stop hidden risks before they turn into agent action

Runtime control

Control the full agent action chain

Agents act at machine speed, without human-level judgment: expanding the blast radius of any error or misuse. Cato controls prompts, responses, tool calls, and tool actions before agents create business impact.

Inspect prompts, responses, tool calls, and tool actions

Block risky actions before they execute

Contain the blast radius of error or misuse

Customer Stories

Customers love Cato

โ€œ

The third layer is agents themselves. We arenโ€™t just talking about employees, but also about agents acting on their behalf. If you can control access and the data the agent accesses, the agent canโ€™t cause much harm if it goes rogue. Thatโ€™s why we focus heavily on identity, permissions, and data boundaries, and Cato AI Security gives us the visibility we need. In summary, each layerโ€”employee AI, product AI, and agentic AIโ€”raises the security bar. Cato AI Security has made managing all of this much easier for us.

Nithin Reddy

VP Security, Dayforce

Nithin Reddy

VP Security, Dayforce

The third layer is agents themselves. We arenโ€™t just talking about employees, but also about agents acting on their behalf. If you can control access and the data the agent accesses, the agent canโ€™t cause much harm if it goes rogue. Thatโ€™s why we focus heavily on identity, permissions, and data boundaries, and Cato AI Security gives us the visibility we need. In summary, each layerโ€”employee AI, product AI, and agentic AIโ€”raises the security bar. Cato AI Security has made managing all of this much easier for us.

Nithin Reddy

VP Security, Dayforce

Doug Innocenti

CIO/CSO, MoonPay

Weโ€™re now securing AI across our employees, our internal tools, and the AI features we ship to customers โ€” with the same level of rigor throughout.

Doug Innocenti

CIO/CSO, MoonPay

Get a live demo

Secure every interaction across the enterprise, cloud, and AI with the only purpose-built SASE platform.

What to expect

15โ€“30 minute session with a SASE product expert

Discuss your use cases and how we can help

Live product demonstration where applicable

Get Started

See Cato in Action

What’s new

AI Security resources in one place

SOLUTION BRIEF

AI Security Solution Brief

WEBINAR

Secure Your AI Transformation

SOLUTION BRIEF

AI Detection Engine Solution Brief

CHECKLIST

What CISOs Must Ask AI Security Vendors

WEBINAR

Defending Against the Next Generation of Agentic Attacks