Agentic Threat Prevention
Predict the attack.
Prevent the breach.
Protect against AI-powered attacks with customized predictions, agentic adaptability, and cloud-native scale.
Today’s Challenges
AI attacks now adapt faster than defenses.


The visibility gap
Agentic attackers identify, chain, and exploit weaknesses to execute sophisticated multi-stage attacks.
Visibility
Adaptation
Volume
Our approach
Stay ahead of AI-powered attacks
Cato Agentic Threat Prevention brings specialized defensive agents into the Single Pass Cloud Engine (SPACE) to anticipate enterprise-specific attack paths, adapt protections autonomously, and scale resources as attack traffic surges. Instead of waiting for manual analysis, static signatures, or appliance updates, Cato adapts prevention to each enterprise’s environment as attacker indicators, behavior, and adaptations change.


Predict based on context
Apply shared context for a holistic view of network assets and security events that drive accurate predictions of attacker’s likely next steps.

Adapt policies autonomously
Adjust policy at machine speed to block predicted actions and disrupt adaptive, multi-stage attacks.

Scale defenses automatically
Expand cloud-based resources on demand as AI-powered attack traffic surges, avoiding appliance limits and protection-depth tradeoffs.
Webinar
Don’t react to AI attacks.
Get ahead of them.
How it works
Agentic Threat Prevention Capabilities
Enterprise-specific threat modeling
Model the attack surface
Customize protection to each enterprise’s real environment, not generic attack patterns.
Model the attack surface through shared context
Combines platform telemetry and threat intelligence
Moves beyond one-size-fits-all detections
Agentic attack-chain reasoning
Anticipate attack paths
Anticipate how AI-powered attackers may combine techniques as attacks unfold.
Identify how separate signals can chain into a successful attack path
Model alternate routes, protocols, pivots, and evasion techniques
Focus on attacker objectives and behaviors, not just known indicators
See it in action
Watch how Cato does it

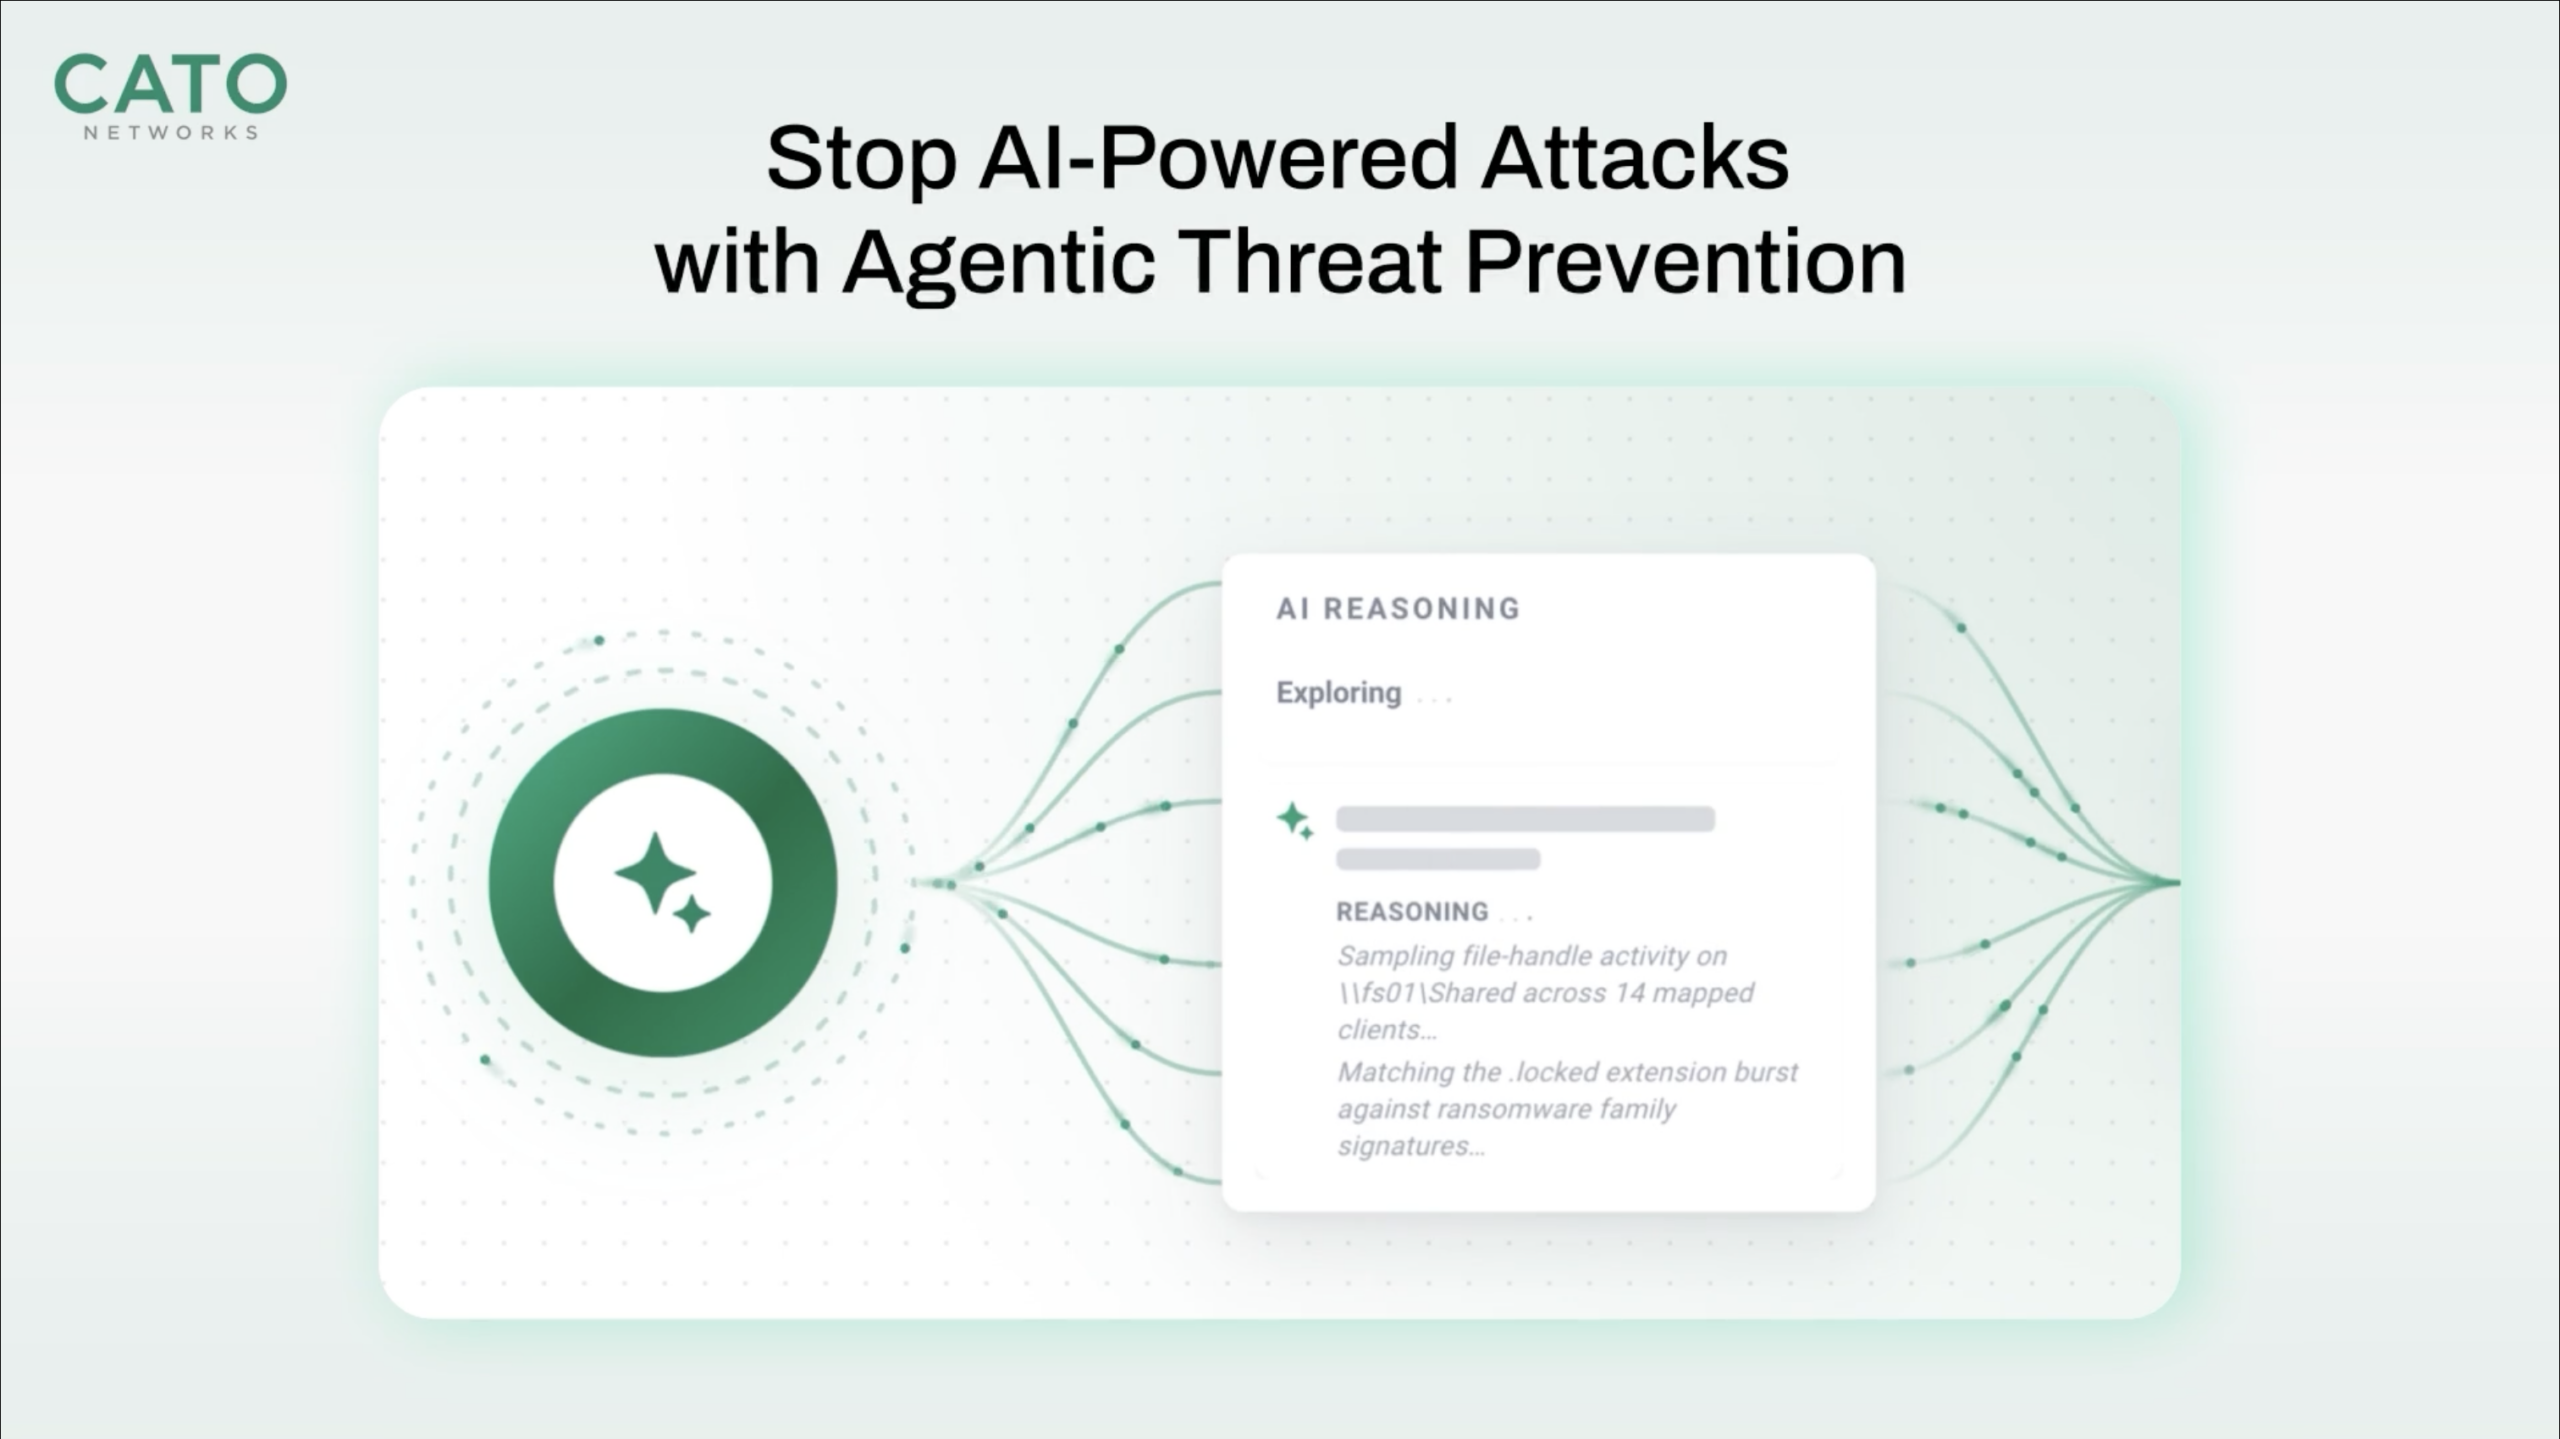
Defending at machine speed: Predict, Adapt, Stop Agentic Attacks
Customer Stories
Customers love Cato
“
Our SOC alerted us to a malware site accessed by one of our users, but when we checked Cato logs, Cato had already blocked the connection before any infection occurred. Cato’s threat prevention worked faster than our external SOC.
Director, IT and Security
Accounting and advisory services firm

Cybersecurity Operations
Global life-saving technology group

IT and Security
Accounting and advisory services firm
Get a live demo
Secure every interaction across the enterprise, cloud, and AI with the only purpose-built SASE platform.
What to expect

15–30 minute session with a SASE product expert

Discuss your use cases and how we can help

Live product demonstration where applicable
Get Started
See Cato in Action
What’s new
AI Security resources in one place


Webinar

Solution Brief
Checklist