AI Security for End Users

Confident AI adoption, without the risk.

Discover shadow AI, inspect every prompt and response, and enforce real-time guardrails.
Decorative concentric ring artwork

Today’s Challenges

Unsecured AI is the new attack surface.
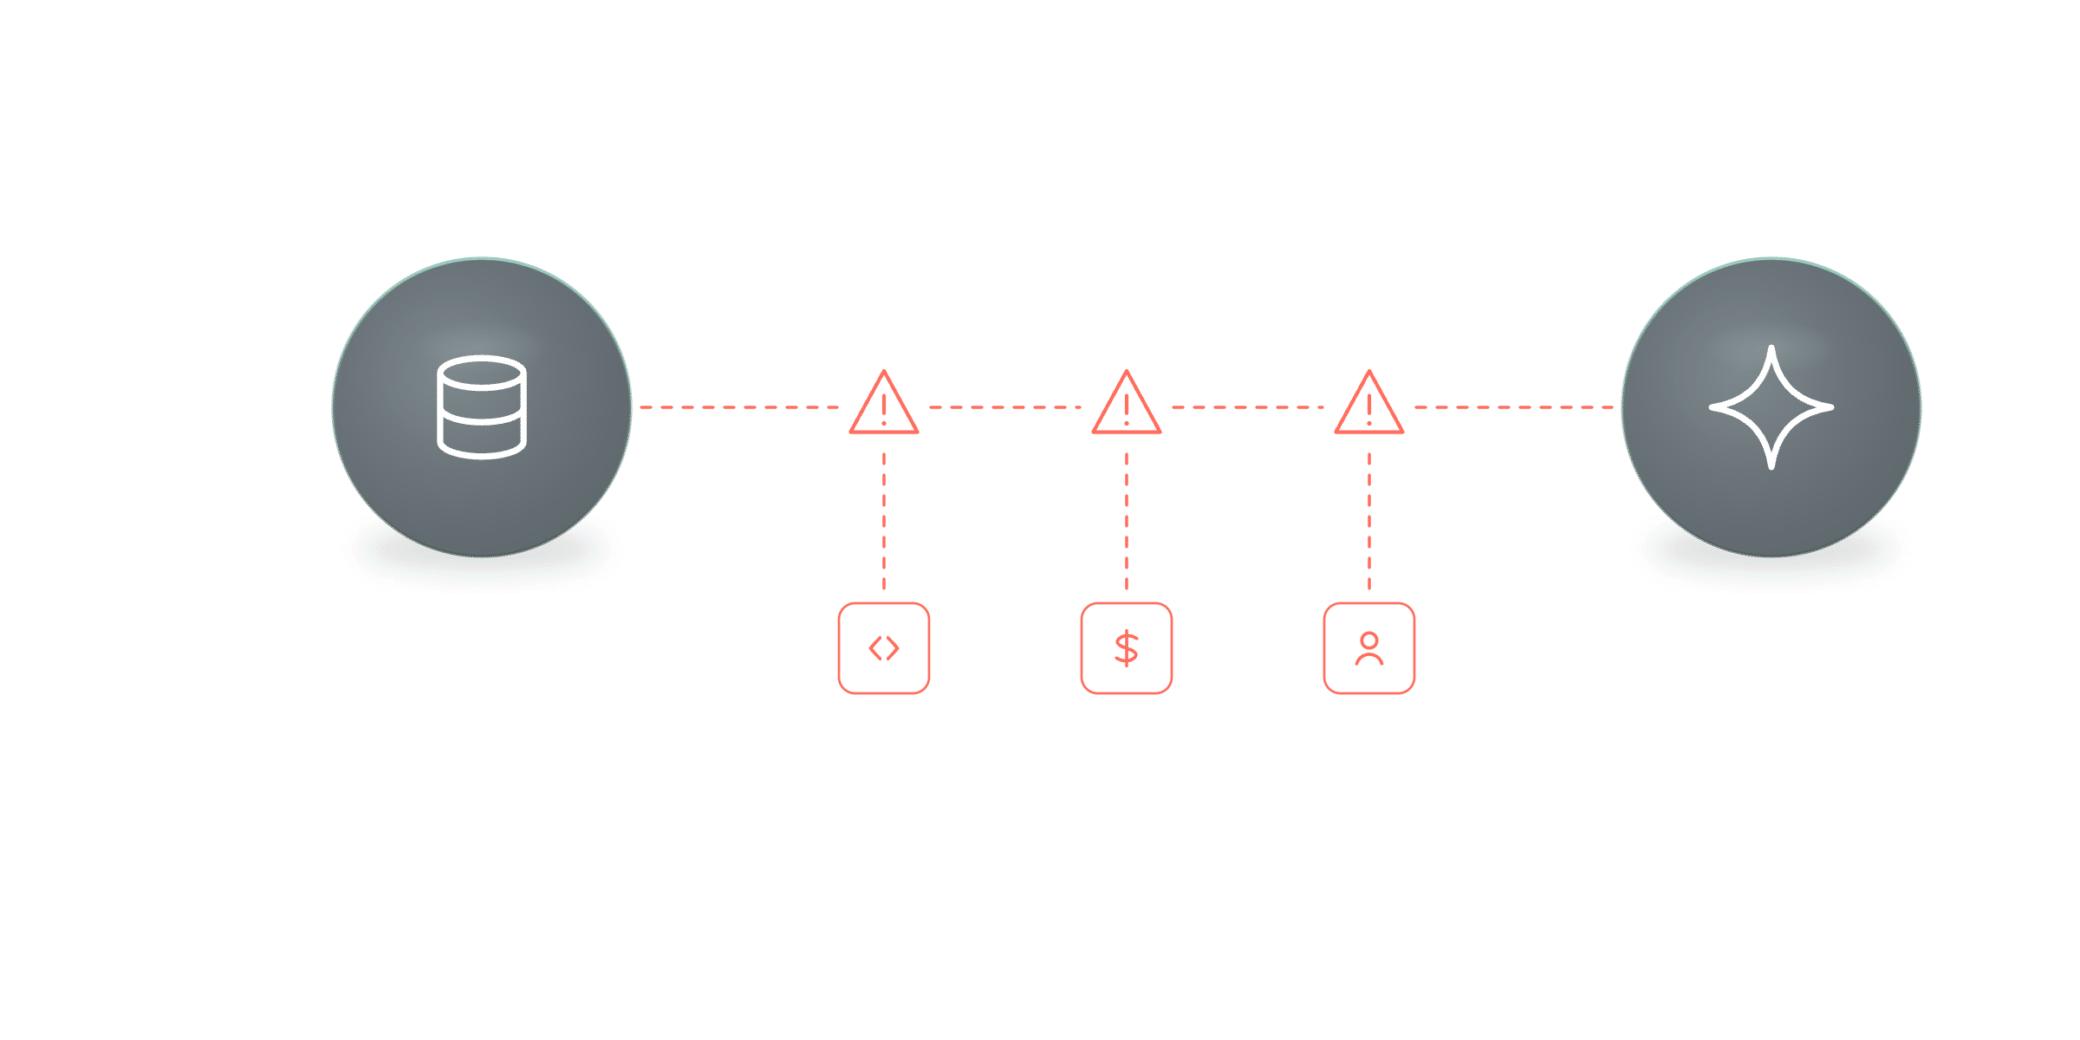
Data exposure
Shadow AI sprawl
Ungoverned agents
Compliance gaps

Data exposure

GenAI apps inadvertently expose sensitive data like IP, source code, financial records, and customer information. Any leak carries real business and compliance risk.

Shadow AI sprawl

Employees adopt unsanctioned AI tools and agents far faster than security can discover, let alone govern, leaving a widening blind spot.

Ungoverned agents

Without evidence of which AI is used, by whom, and against which regulated data, every audit becomes a scramble, and every gap a liability.

Compliance gaps

Without evidence of which AI is used, by whom, and against which regulated data, every audit becomes a scramble β€” and every gap a liability.

Data exposure

Shadow AI

Ungoverned agents

Compliance gaps

Our approach

Let employees use AI
without losing control.

Employees already use AI tools every day, with or without approval. Cato gives you visibility into that usage and enforces guardrails on what data can flow to which models, so people stay productive while sensitive data stays protected.

Play the video

Discover shadow AI

Cato automatically inventories every sanctioned and unsanctioned AI app, model, and agent in use across every user and site.

Semantically analyze prompts

Cato reads the intent of every prompt, response, and action in real time to catch sensitive data and risky behavior, beyond keywords.

Enforce real-time guardrails

Cato blocks misuse and redacts sensitive data inline, so people keep working and your data stays where it belongs.

EBOOK

CISO Six-Step Plan for Secure AI Transformation

How it works

AI Security for End Users Capabilities

Discover Shadow AI

See every AI in use

Get immediate visibility into sanctioned and unsanctioned AI tools and agents across the organization.

Auto-inventory every 3rd-party AI tool, copilot, and agent

Assess risk and surface governance blindspots

Map usage to users, apps, and data β€” agentless

Assess AI risk in context

Prioritize the AI risks that matter

Analyze AI usage across users, tools, prompts, and agents to identify risky behavior before it becomes exposure.

Risk scoring across sanctioned and shadow AI

Usage patterns mapped to security impact

Actionable insights for policy and control decisions

Align to corporate governance frameworks

Stay compliant by design

Map AI usage to corporate guidelines and standards like EU AI Act, GDPR, NIST, and OWASP.

Define what’s allowed, restricted, or monitored

Consistent rules for both users and agents

Auditable, enforceable evidence

Enforce AI policies in real time

Stop data leaks as they happen

Inspect prompts, responses, and agentic actions as they happen and act before data leaves.

Enforce custom AI policies on every interaction

Automatically block or redact sensitive data

Redirect users to approved tools

Log violations for auditable evidence

Govern agentic actions & workflows

Keep AI agents in bounds

Discover agents and MCP servers, then block risky prompts, actions, and tool calls.

Profile MCP servers and tool calls

Block or redact unsafe prompts and behaviors

Preserve full audit trails for investigation

Protect source code and IP leakage in coding agents

See it in action

Watch how Cato does it

Control How Your Enterprise Uses AI

Control How Your Enterprise Uses AI

Video

See how Cato discovers the AI your people already use, inspects every prompt, response, and upload in real time, and enforces guardrails inline β€” natively in the SASE Cloud.

Video

Play the video

Customer Stories

Customers love Cato

β€œ

We prioritized the AI our employees use, so we deployed Cato AI extensions for visibility and to prevent prompt injection and data leakage. Then, as we built our own AI features, we put Cato AI security inline so it catches unintentional data leakage and prevents exposing sensitive data to models while still meeting our SLAs.

Nithin Reddy

VP Security, Dayforce

Nithin Reddy

VP Security, Dayforce

We prioritized the AI our employees use, so we deployed Cato AI extensions for visibility and to prevent prompt injection and data leakage. Then, as we built our own AI features, we put Cato AI security inline so it catches unintentional data leakage and prevents exposing sensitive data to models while still meeting our SLAs.

Nithin Reddy

VP Security, Dayforce

Chidi Alams

Chief Information Officer, Just Born Inc

Cato AI Security gives us visibility into what’s actually happening with AI across the enterprise. That’s the foundation for everything else β€” policy, training, investment decisions. Without it, you’re managing risk you can’t see.

Chidi Alams

Chief Information Officer, Just Born Inc

Security Leader

Global Industrial Technology Company

I was referring to controls designed to put guardrails around allowable prompt usage, both input and output. Cato’s mechanism leverages the same policy set across endpoint AI usage capabilities and any agentic controls we implement for our own tools, providing guardrails around activity via NCP gateways.

Security Leader

Global Industrial Technology Company

Doug Innocenti

CIO/CSO, MoonPay

Because Cato sits at the top of the network, it catches every AI interaction β€” every prompt, every response β€” no matter how it’s generated. That’s exactly where AI security needs to be.

Doug Innocenti

CIO/CSO, MoonPay

Get a live demo

Secure every interaction across the enterprise, cloud, and AI with the only purpose-built SASE platform.

What to expect

15–30 minute session with a SASE product expert

Discuss your use cases and how we can help

Live product demonstration where applicable

Get Started

See Cato in Action

What’s new

AI Security resources in one place

SOLUTION BRIEF

AI Security Solution Brief

WEBINAR

Secure Your AI Transformation

SOLUTION BRIEF

AI Detection Engine Solution Brief

CHECKLIST

What CISOs Must Ask AI Security Vendors