AI Security
Protect your business from
AI risk, wherever it is.
On the endpoint, in SaaS and in the cloud. Managed from one console.
Today’s Challenges
AI is everywhere in your enterprise. Most of it is ungoverned.
For users
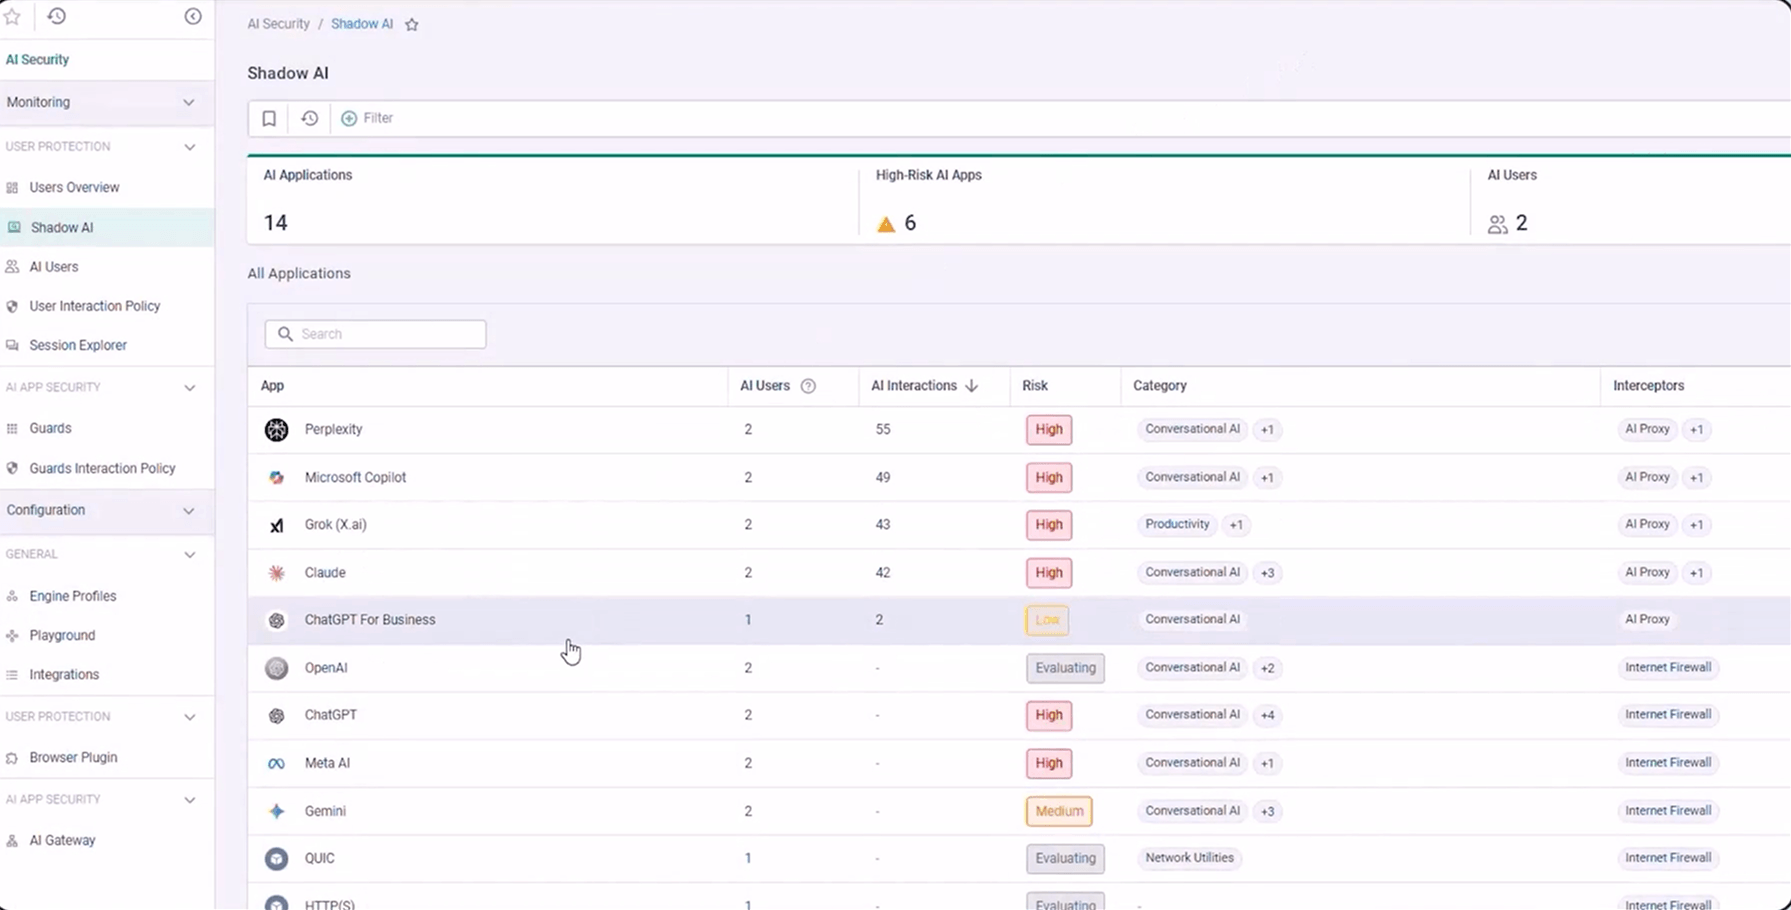
Shadow AI
Teams adopt AI tools and agents faster than security can find them.

For applications
AI-specific attacks
Prompt injection and jailbreaks target the AI apps your teams build.
For agents
Ungoverned agents
Agents act across tools, data and workflows without dedicated controls.
Our approach
Breadth and depth of
AI security in one view.
Three use cases span visibility, posture, and runtime control. One AI-native engine and one console cover all three, whether AI runs on the endpoint, in SaaS, or in apps you host yourself.


Visibility
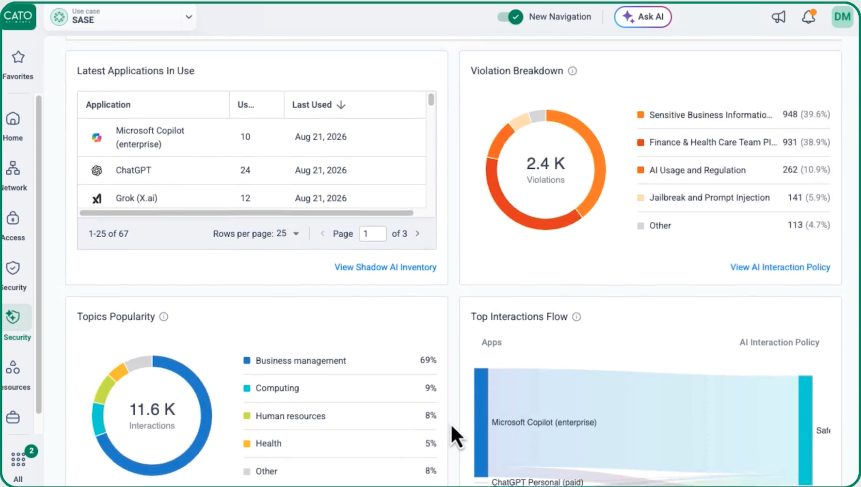
Discover shadow AI and coding agents across endpoints
Inventory LLMs and RAG apps
Map agents, MCP servers and skills
Posture
Classify app risk
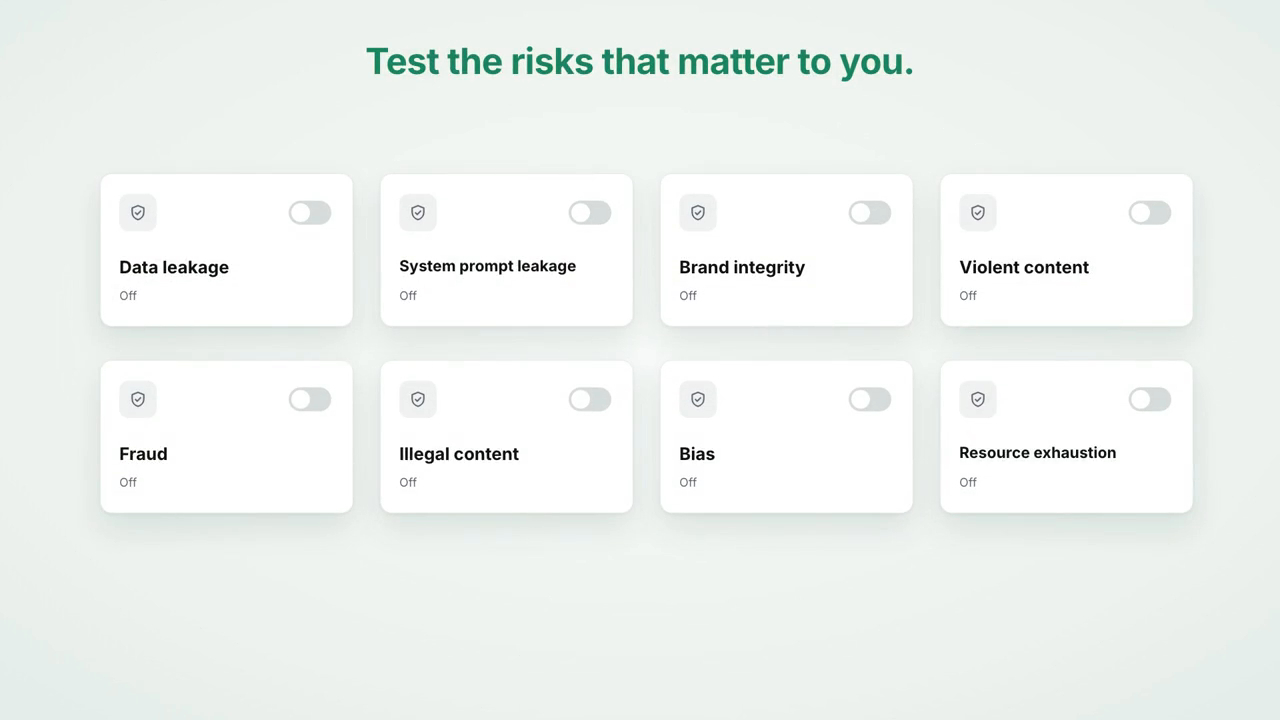
Red team AI apps
Track data flows and supply chain risk
Red team AI agents
Profile agent actions and risk
Runtime control
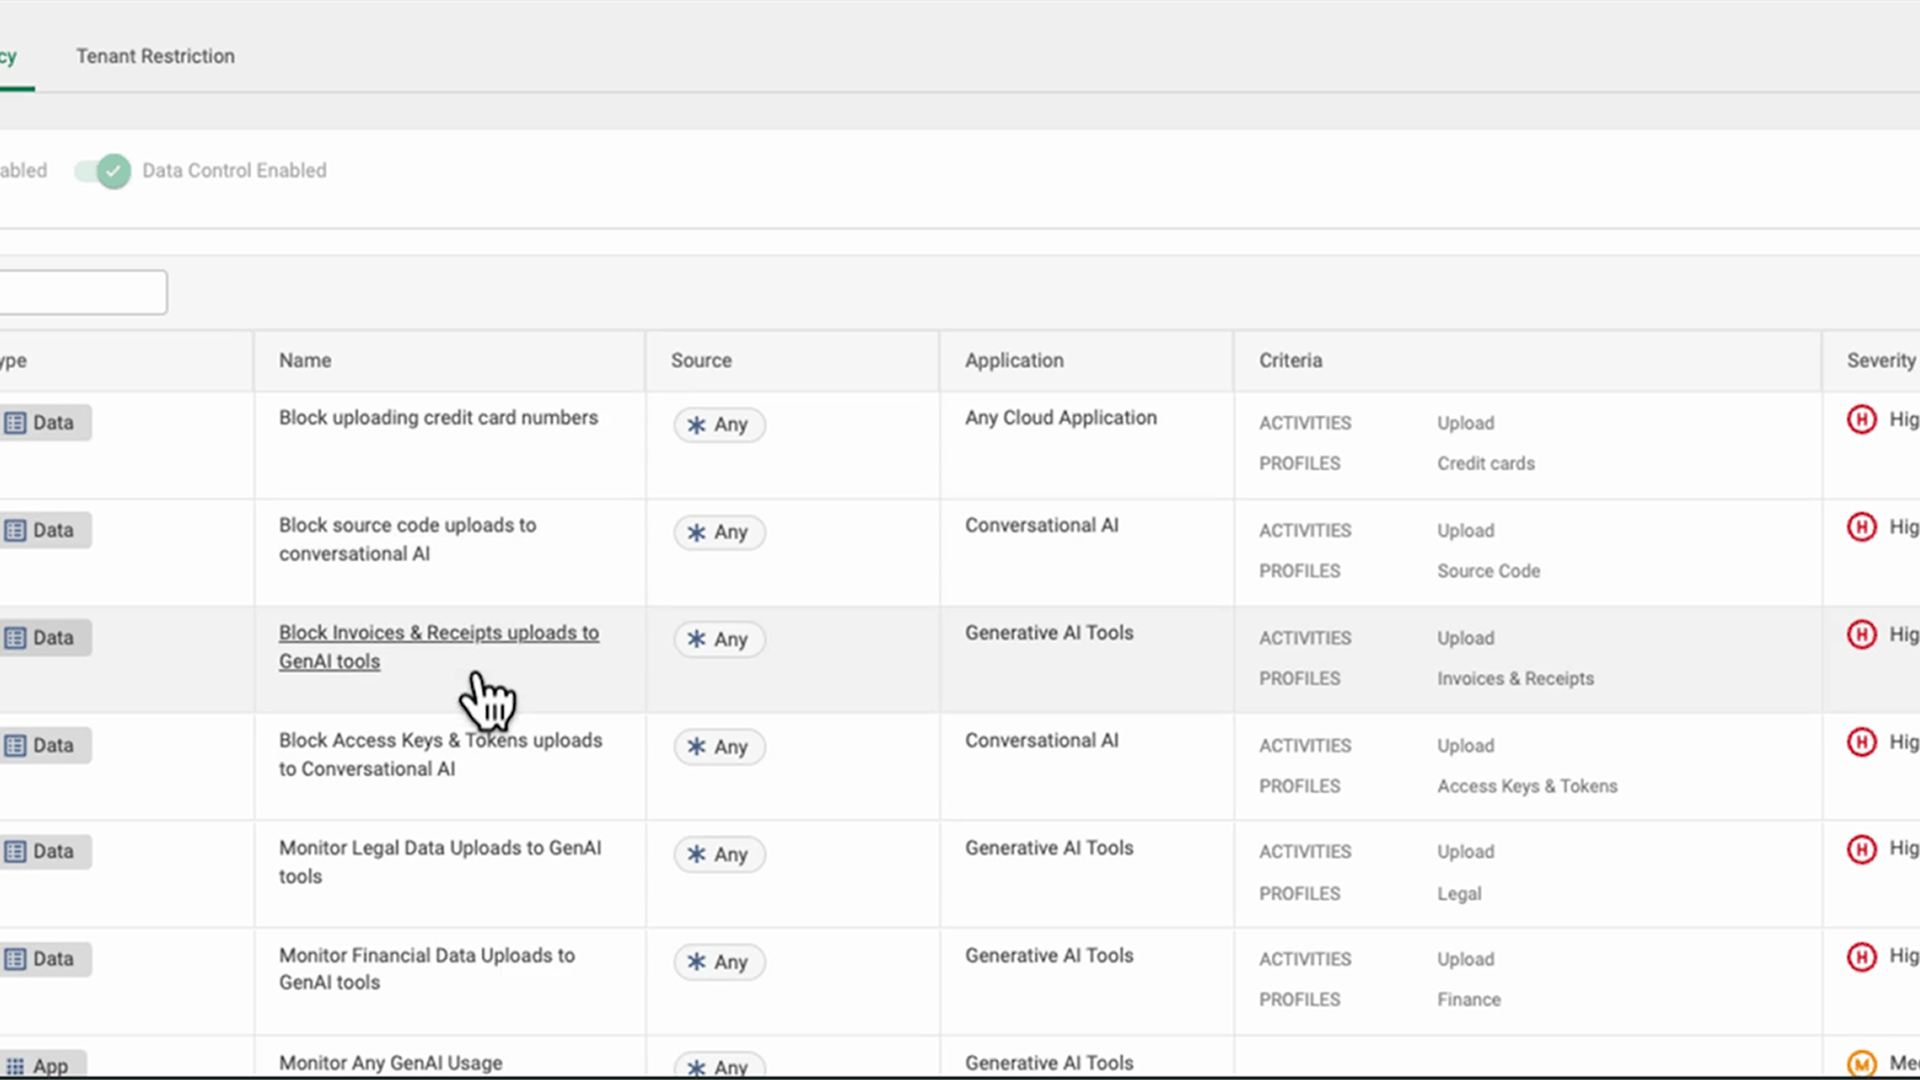
Stop data leaks in prompts
Block prompt injection and jailbreaks
Stop risky coding-agent tool calls before they run
Covers coding agents on the endpoint and AI apps in the browser, with enforcement for Claude Code, Cursor, and Codex.
Protects apps through the Cato cloud, the AI gateway you already run, or on-prem with Outposts.
The same engine that protects users and apps inspects agent prompts, responses, and tool calls.
The engine
Every interaction gets
the level of inspection it needs.
One AI-native engine supports all three use cases, checking every interaction inline and going deeper only when needed.
Reads prompts, responses and tool calls
Keeps context across the conversation
Uses live attack research to inform detection
Every interaction
Fast checks · milliseconds
The ones that need a closer look
Purpose-built models
Rare edge cases
Deep reasoning
Your policy decides
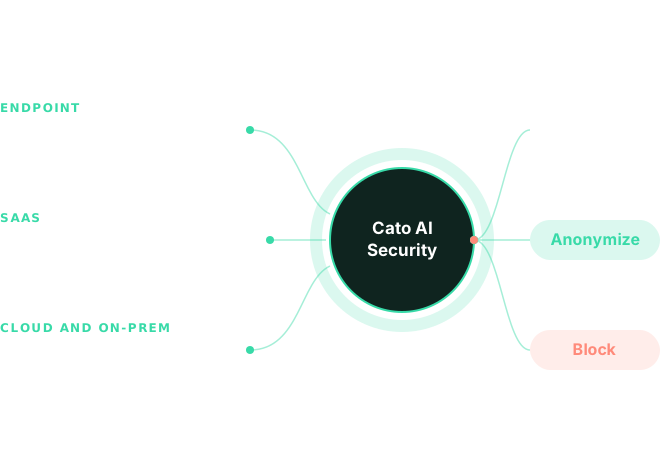
Monitor
Anonymize
Block
eBook
CISO Six-Step Plan for Secure AI Transformation
Why Cato
Networking, security and AI security on one platform.

One console
Discovery, policy and enforcement for users, applications and agents in one place.

Inline inspection
Prompts, responses and tool calls are inspected in real time, in the path.

Shared context
AI activity is correlated with network, CASB, endpoint and user behavior.

One data lake
AI and security events sit together for audit, analytics and response.

Deploy your way
Run AI Security for Applications on-prem or in your own cloud with AI Security Outposts. Prompts stay in your environment.
See it in action
Watch how Cato does it

Secure Enterprise AI Innovation

Shadow AI is Everywhere.
Control How Your Enterprise Uses AI
Red Team: Test Your AI Models
One platform
Start anywhere. Grow everywhere.
Start with AI Security and expand seamlessly on the same Cato SASE Platform, without adding point products or operational complexity.

You are here
AI Security

SASE Convergence
One converged platform

Zero Trust Security
Adaptive, risk-based policy

Universal ZTNA
Secure access everywhere

Next Gen Networking
Global private backbone

Cato XOps
Unified XDR and AIOps
Customer Stories
Customers love Cato
“
Having the right AI security solution gave me the confidence to say yes to the business. It didn’t just protect us — it accelerated our AI adoption because I could enable our teams instead of blocking them.
Doug Innocenti
CIO/CSO, MoonPay

Alfred Sobrinho
CIO, PlayPower

Chidi Alams
Chief Information Officer, Just Born Inc
Nick Hidalgo
VP, Information Technology, Redner’s Markets
Guy Pascarello
VP, Information Technology, AKRF
Get a live demo
Secure every interaction across the enterprise, cloud and AI on one platform.
What to expect

15–30 minute session with a SASE product expert

Discuss your use cases and how we can help

Live product demonstration
Get Started
See Cato in Action
What’s new
AI Security resources in one place


SOLUTION BRIEF
AI Security Solution Brief
WEBINAR
Secure Your AI Transformation
SOLUTION BRIEF
AI Detection Engine Solution Brief
CHECKLIST
What CISOs Must Ask AI Security Vendors
FAQS
Answers to common questions
Overview and AI Risk2 questions
What is Cato AI Security?
Cato AI Security is Cato’s solution for governing and protecting enterprise AI across users, applications, and agents. It helps security teams see which AI tools are being used, control how sensitive data is handled in AI interactions, and apply policy to AI interactions, agents, and workflows without forcing the business to choose between AI adoption and security oversight.
What AI risks is Cato AI Security designed to address?
Cato focuses on three practical AI security problems: shadow AI, data exposure, and agentic risk. Shadow AI appears when employees use unapproved AI tools or launch AI-powered applications and agents. Data exposure happens when prompts, uploads, outputs, or tool calls expose sensitive information to AI tools. Agent risk grows when AI-powered agents act autonomously, using data and tools, without consistent policy and monitoring.
Discovery, Data, and Agents3 questions
How does Cato help discover shadow AI?
Cato identifies AI applications, embedded AI features, and AI agents across the enterprise, including tools that were not formally approved. The goal is not simply to block everything. It gives security teams the visibility they need to understand what AI exists in the enterprise, who is using it or building with it, what the risk level is, and which activity may require policy, education, or stronger controls.
How does Cato reduce the risk of sensitive data exposure?
Cato applies security controls to AI interactions so sensitive data is less likely to leave the organization through prompts, uploads, responses, or agent activity. That matters because AI risk often appears in normal workflows and interactions: a user pastes source code into a chatbot, uploads a customer file, or connects tools and agents to systems that contain regulated or confidential data.
How does Cato secure AI agents?
Cato AI Security for Agents gives teams visibility and control over agents that can access tools, data, and systems. It can discover local agents and connected MCP servers, help profile agentic risk, and apply runtime protection to prompts, model outputs, tool calls, and tool messages. That gives security teams a way to govern agentic AI without treating every agent as a one-off exception.
Platform and Fit3 questions
How is Cato AI Security different from using point tools?
Point tools can help with a narrow slice of AI security, but they often leave separate views for users, applications, agents, network traffic, and data policy. This creates operational complexity, as teams manage separate tools for each type of AI activity. Beyond AI, Cato AI Security is built into the Cato SASE Platform, so AI governance sits alongside networking, access, and security policy in one platform. By combining AI activity with network, CASB, endpoint, and behavioral telemetry, Cato improves detection accuracy and provides a broader investigation context.
Who is Cato AI Security designed for?
It is designed for security, AI governance, and risk leaders who need to let the business use AI while maintaining control over data, access, and agent behavior. It is especially relevant for organizations already seeing unsanctioned AI tools, developer agents, MCP servers, embedded SaaS AI features, or AI workflows that are moving faster than existing governance processes.
Does Cato AI Security fit into the broader Cato platform?
Yes. Cato AI Security is one of the converged solutions on the Cato SASE Platform. Organizations can start with AI Security and later expand into related capabilities such as Zero Trust Security, Universal ZTNA, Next Gen Networking, or SASE Convergence without moving to a separate architecture.


